Establish trust boundaries
Separate carriers, enterprise systems, mission networks and legacy voice domains through explicit SBC policy.
Apply secure SIP edge controls, controlled interconnection and resilient deployment principles to defence communications.
Apply secure SIP demarcation, controlled interconnection and resilient deployment principles to defence voice environments, with solution scope governed by the applicable security authority.
Separate carriers, enterprise systems, mission networks and legacy voice domains through explicit SBC policy.
Normalize signaling and route approved calls between diverse systems without exposing internal topology.
Define survivability, management access, software lifecycle, configuration custody and escalation.
Download the PDF files directly. Use the documentation portal for configuration guides, installation procedures and release-specific information.
A starting point for your project. Review the model data sheet before ordering.
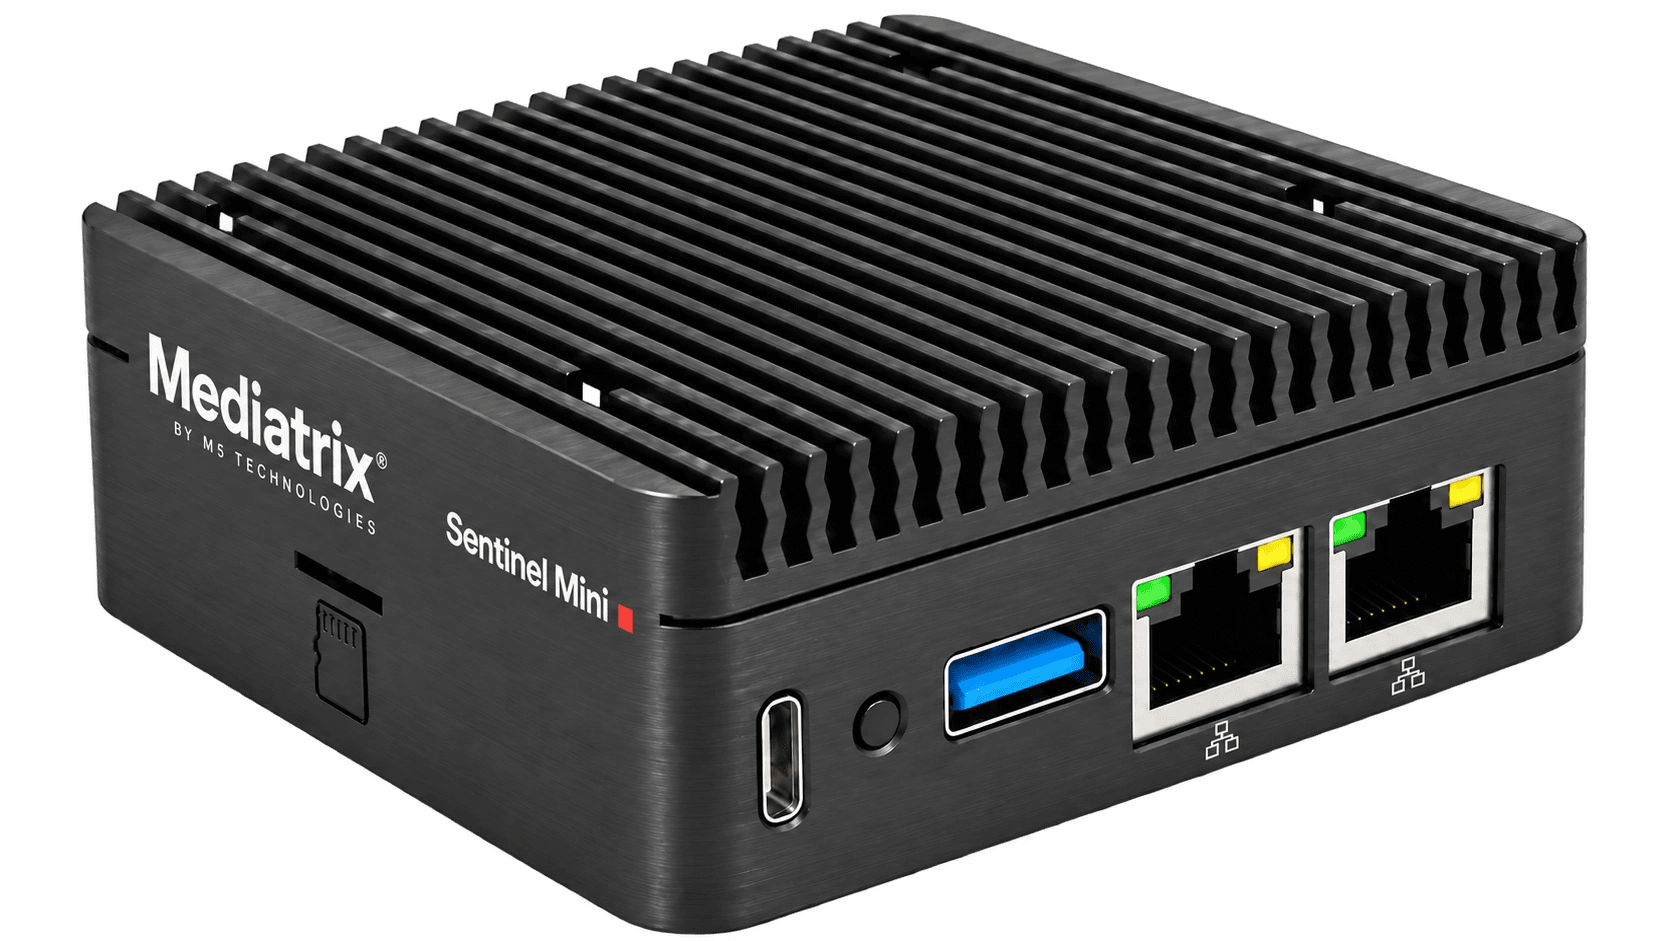
A compact SBC for a branch or a dedicated SIP edge.
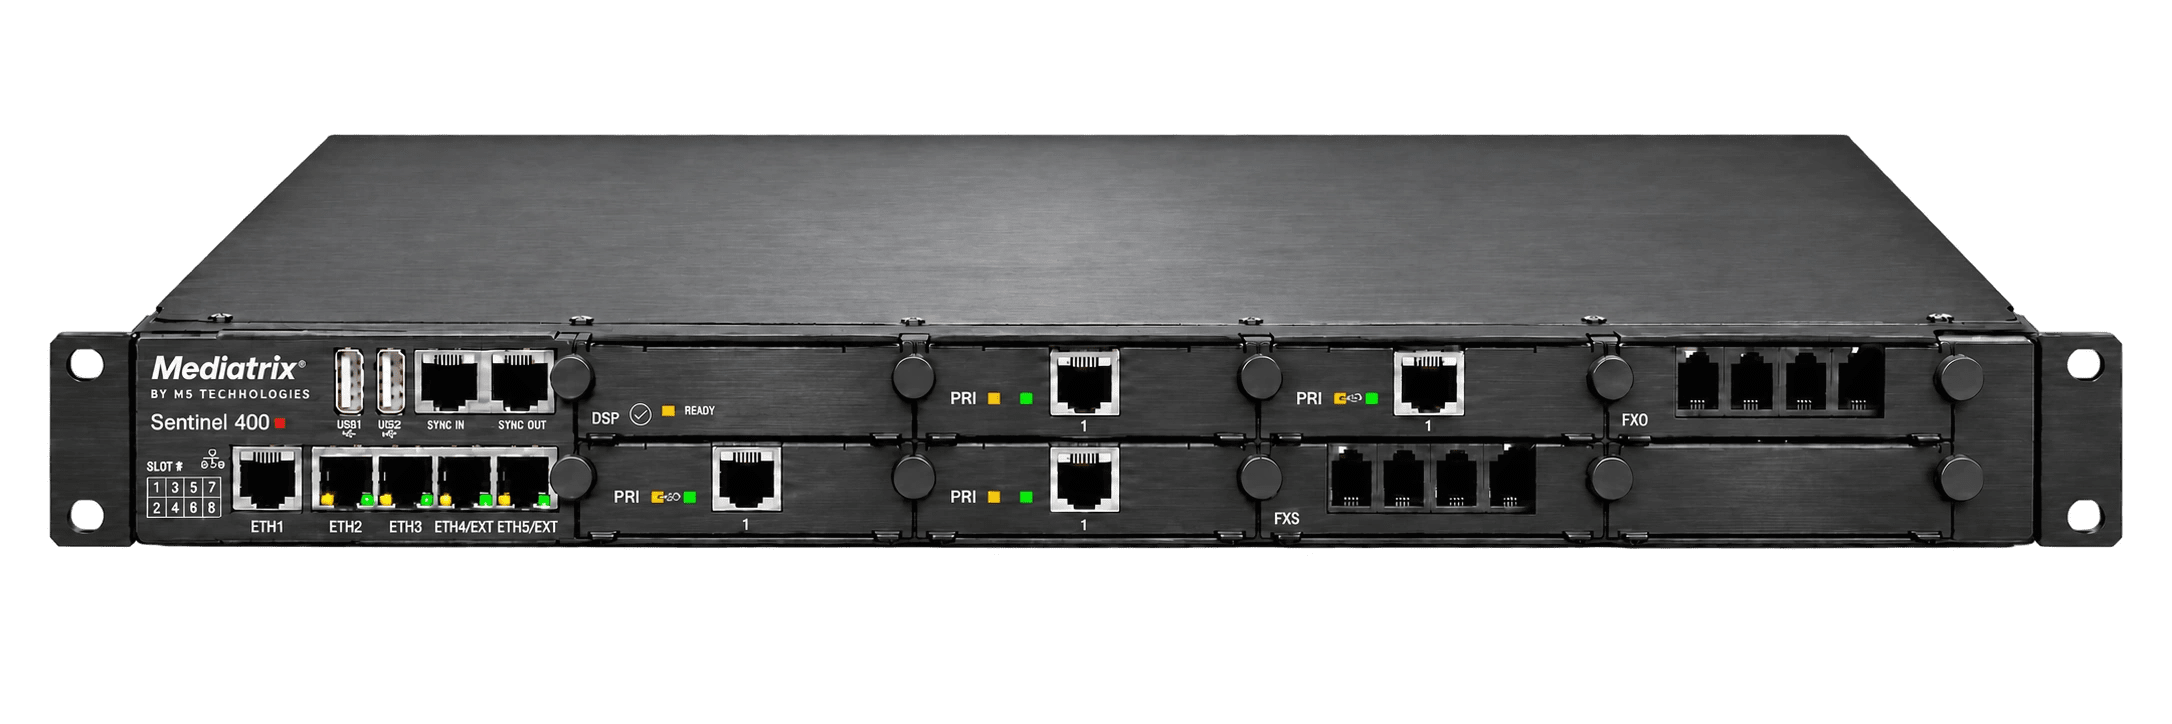
A modular voice edge for sites with mixed telephony interfaces.
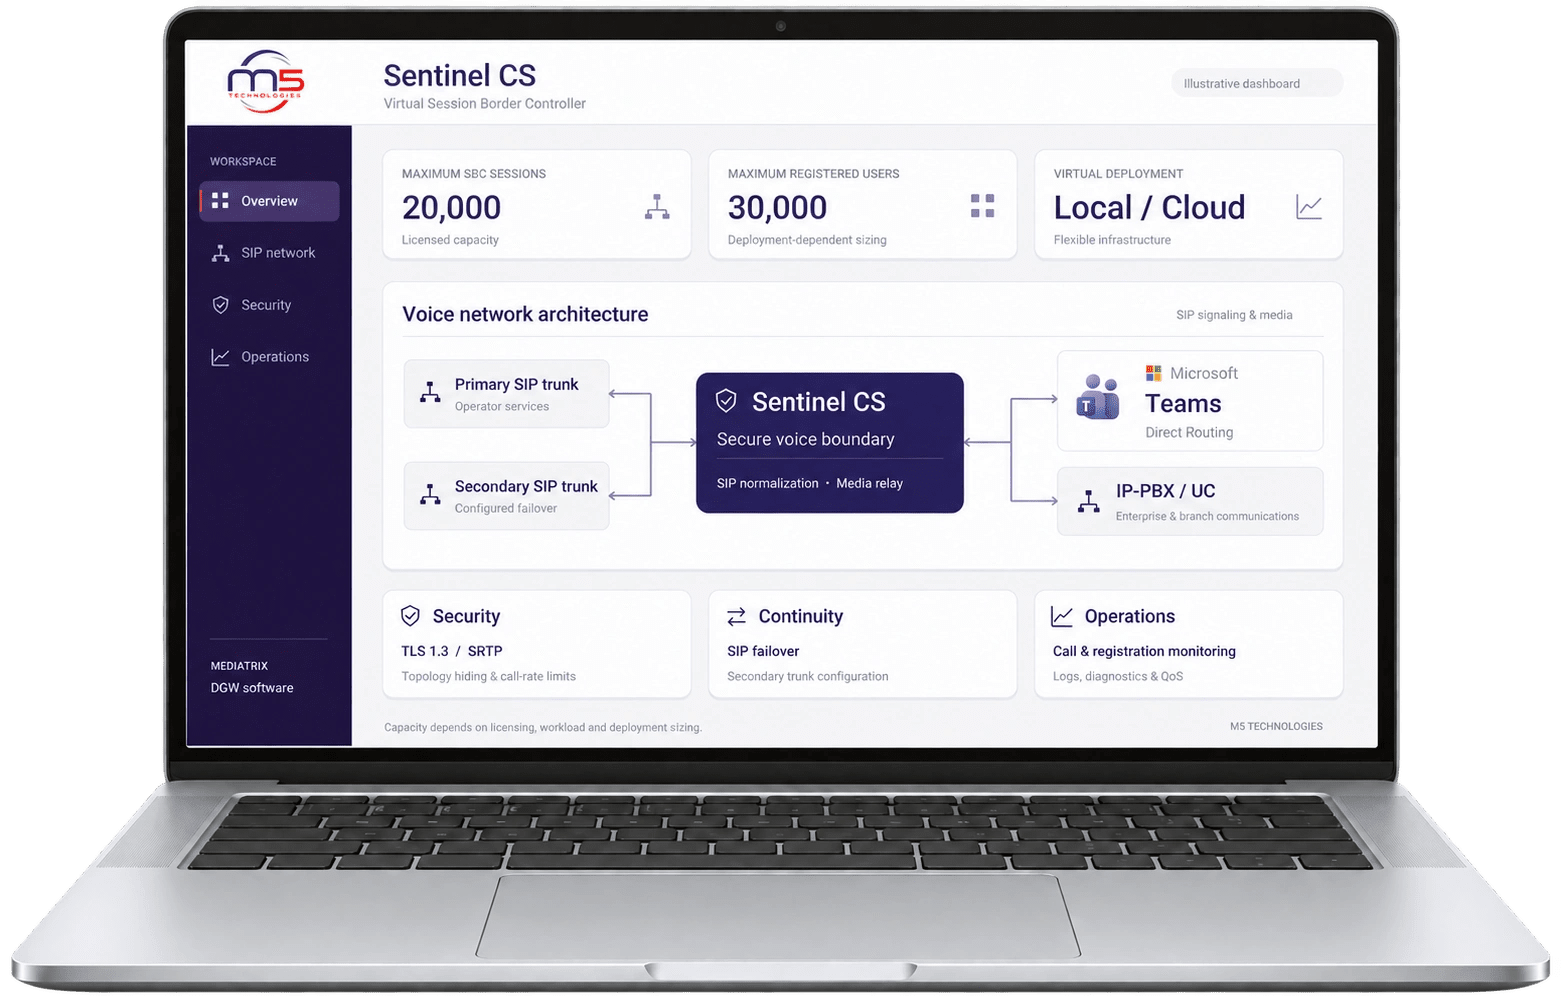
An SBC deployed on your virtual infrastructure.
The M5 layer sits between what must be preserved and the destination architecture, making security, translation and failure behavior explicit.
Local phones, a local IP PBX, Mediatrix gateways and Sentinel can exchange SIP calls entirely inside the organization. The voice path can remain on a private LAN, VLAN, campus network or isolated operational network.
An external connection is used only when calls must reach public numbers, remote sites or hosted services. If the required call path is entirely local, the system can stay on the private network.
Local users and systems require an explicit primary call path.
Operational communications need their own priority, security and recovery rules.
Legacy or safety endpoints remain isolated until compatibility is proven.
Sentinel, Mediatrix and DGW controls are selected around the actual communications dependency.
Central call control, Teams or management services connect through a protected route.
External reachability includes a tested alternate path where continuity requires it.
Reference flow — carrier, platform, jurisdiction and field requirements determine the production design.
Use these checkpoints to evaluate a telecom security for defence project before product selection or cutover.
The recommended design depends on the deployed carrier, PBX or UC platform, interfaces, call volume, failure modes and regulatory context.| Decision area | Uncontrolled approach | M5 architecture | Acceptance evidence |
|---|---|---|---|
| Interoperability | Assume systems will connect | Normalize signaling and media at a defined boundary | Documented end-to-end call tests |
| Security | Expose internal voice domains | Apply identity, topology and transport controls | Approved routes, certificates and logs |
| Continuity | Cut over every site together | Preserve required services and phase migration | Failover, rollback and exception tests |
| Operations | Treat go-live as the finish line | Assign monitoring, updates and escalation ownership | Runbook, backups and support entitlement |
Share the product, deployment and target outcome. M5 will identify the right technical and commercial path.