Secure demarcation
Hide internal topology and credentials while inspecting and authorizing inbound and outbound sessions.
Protect SIP trunks with policy enforcement, encryption, topology hiding, normalization and controlled interconnection.
Create a controlled demarcation point between carrier SIP trunks and enterprise communications with policy enforcement, normalization, encryption and topology protection.
Hide internal topology and credentials while inspecting and authorizing inbound and outbound sessions.
Adapt carrier, PBX and UC signaling through rule-based routing and header manipulation.
Apply call admission control, QoS, traffic shaping, monitoring and failover policies.
Download the PDF files directly. Use the documentation portal for configuration guides, installation procedures and release-specific information.
A starting point for your project. Review the model data sheet before ordering.
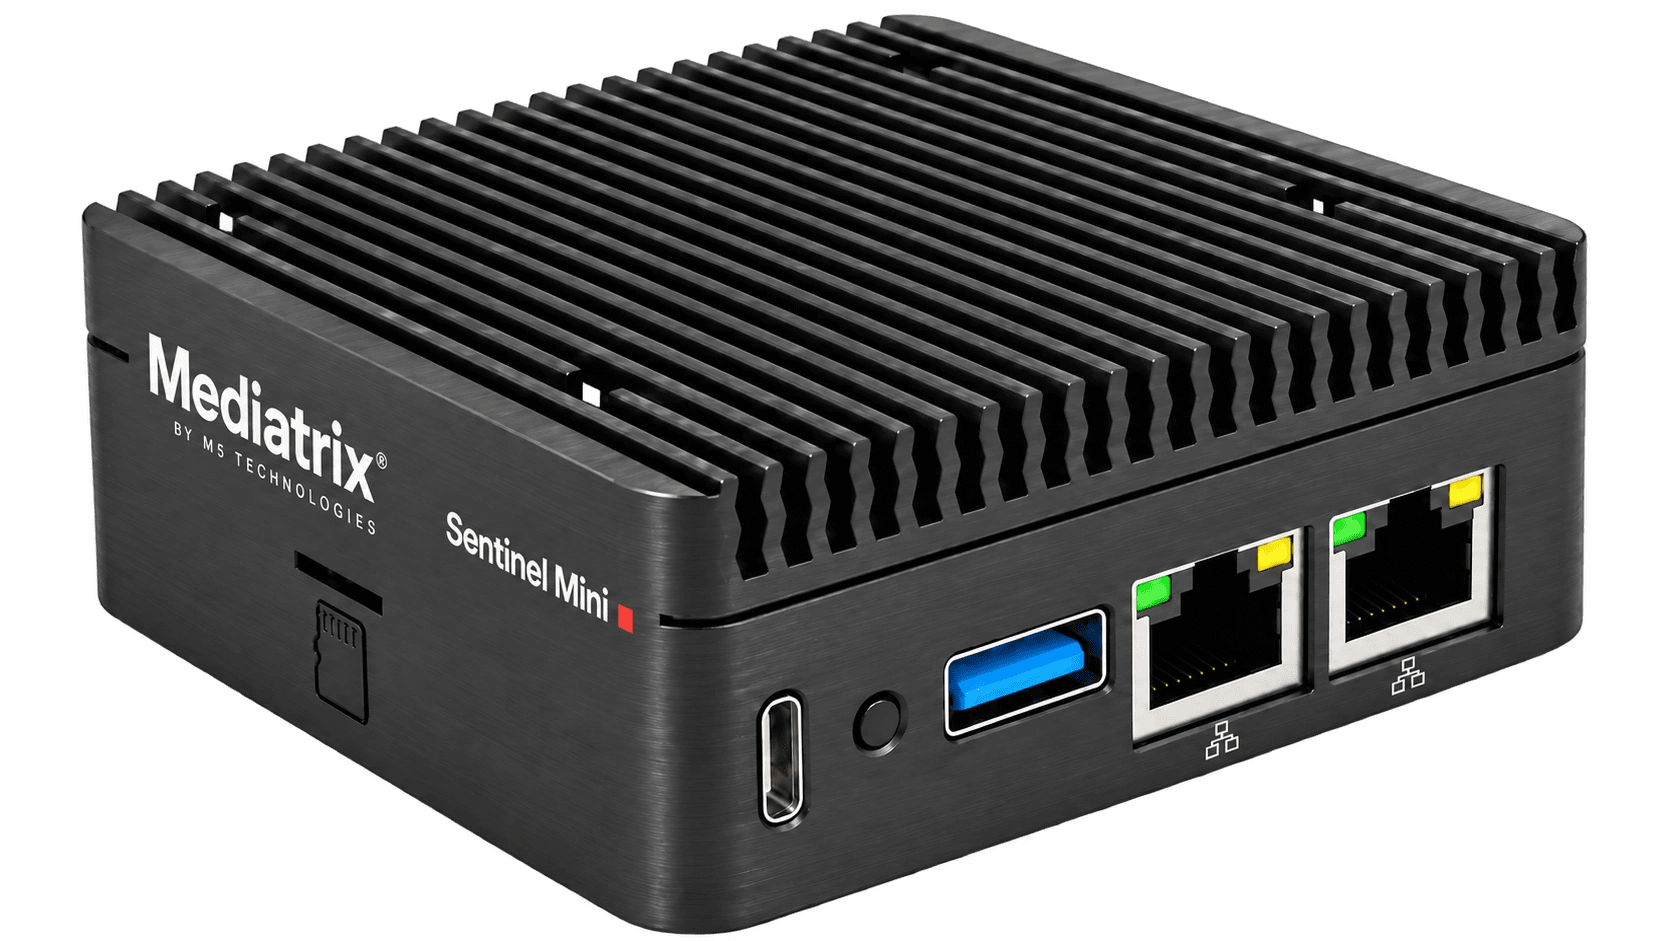
A compact SBC for a branch or a dedicated SIP edge.
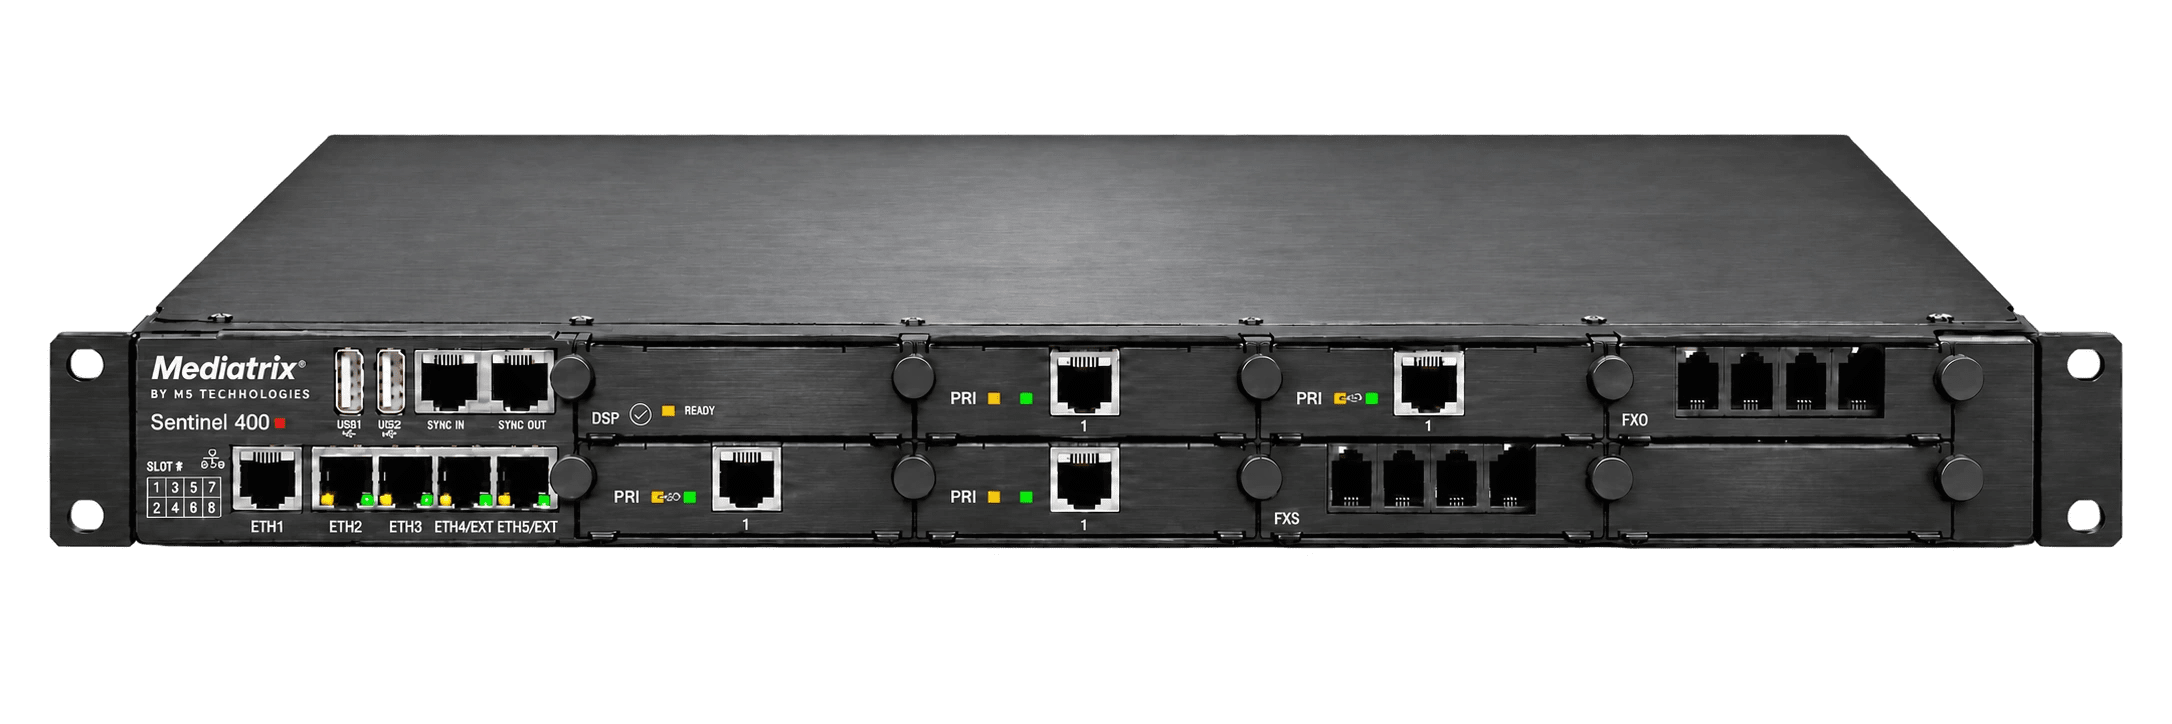
A modular voice edge for sites with mixed telephony interfaces.
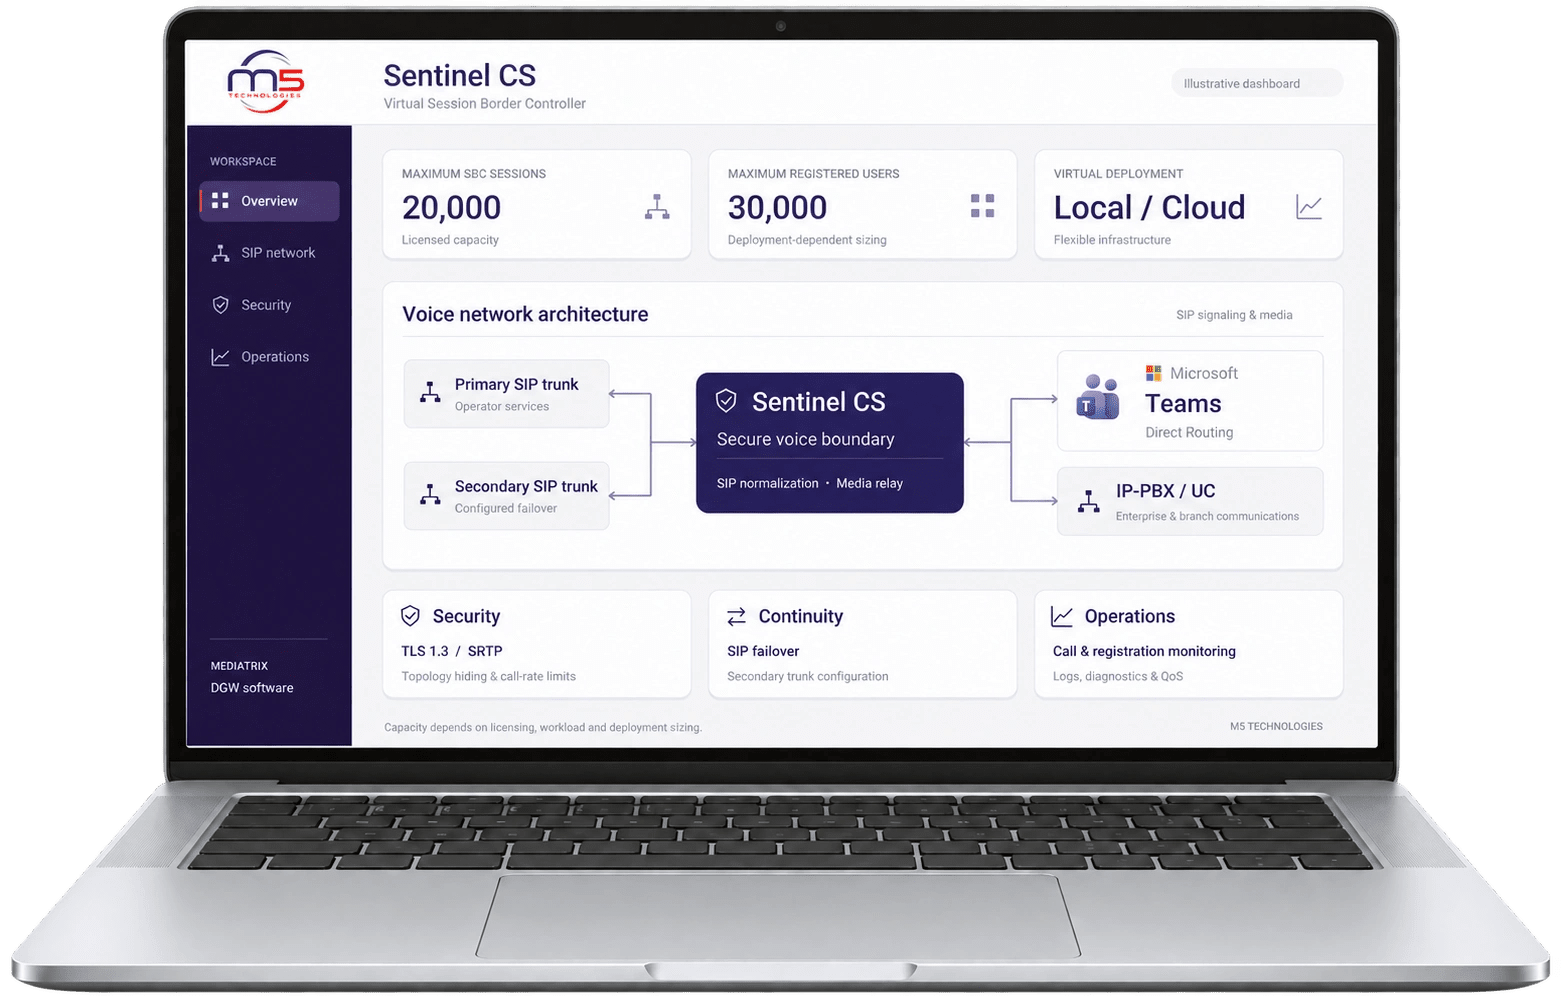
An SBC deployed on your virtual infrastructure.
The M5 layer sits between what must be preserved and the destination architecture, making security, translation and failure behavior explicit.
Local phones, a local IP PBX, Mediatrix gateways and Sentinel can exchange SIP calls entirely inside the organization. The voice path can remain on a private LAN, VLAN, campus network or isolated operational network.
The carrier path is needed only for calls that leave the private voice domain or arrive from public telephone numbers. Internal extension-to-extension calls can stay local.
Provides an alternate route only when failover is designed and tested.
Owns extensions, call features and internal dial plans.
Place and receive calls through the enterprise platform.
Reviews alarms, call records, certificates and configuration state.
Creates a controlled demarcation for identity, routes, media, capacity and failure behavior.
Delivers public calling with its own SIP profile and routing rules.
Reference flow — carrier, platform, jurisdiction and field requirements determine the production design.
Use these checkpoints to evaluate a secure sip trunking project before product selection or cutover.
The recommended design depends on the deployed carrier, PBX or UC platform, interfaces, call volume, failure modes and regulatory context.| Decision area | Uncontrolled approach | M5 architecture | Acceptance evidence |
|---|---|---|---|
| Interoperability | Assume systems will connect | Normalize signaling and media at a defined boundary | Documented end-to-end call tests |
| Security | Expose internal voice domains | Apply identity, topology and transport controls | Approved routes, certificates and logs |
| Continuity | Cut over every site together | Preserve required services and phase migration | Failover, rollback and exception tests |
| Operations | Treat go-live as the finish line | Assign monitoring, updates and escalation ownership | Runbook, backups and support entitlement |
Share the product, deployment and target outcome. M5 will identify the right technical and commercial path.